CRM
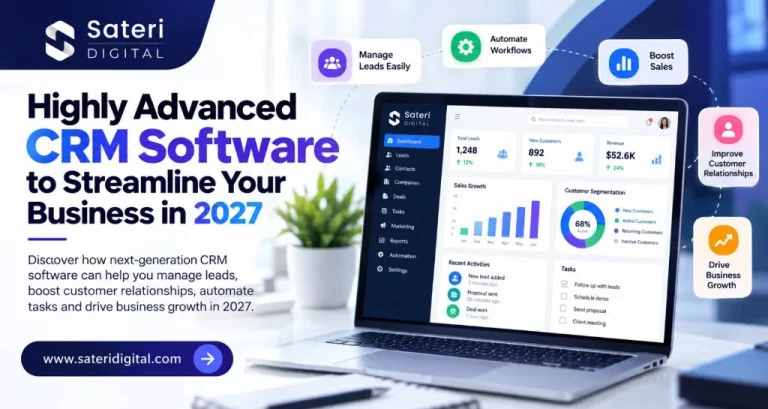
Highly Advanced CRM Software to Streamline Your Business in 2027
Find the best way to choose suitable CRM software to manage your business.
October 2026Essential controls for health tech platforms handling protected patient data.
Building healthcare software that handles protected health information (PHI) requires more than encryption and a privacy policy. HIPAA compliance spans technical safeguards, administrative policies, vendor contracts, and ongoing audit readiness. Whether you are launching a patient portal, telehealth platform, or clinical workflow tool, this checklist covers what engineering and product teams must get right.
Designate a security officer, conduct workforce HIPAA training, and maintain documented policies for access, incident response, and breach notification. Business associate agreements (BAAs) are required with every cloud provider, analytics vendor, and subprocessors that touch PHI.
Encrypt PHI at rest (AES-256) and in transit (TLS 1.2+). Implement unique user IDs, automatic logoff, and audit controls that record who accessed which records and when. Role-based access ensures clinicians, billing staff, and administrators see only what their job requires.
Validate inputs to prevent injection attacks. Sanitize outputs displayed in patient-facing UIs. Session management must resist fixation and hijacking. APIs exposing PHI need OAuth 2.0, scoped tokens, and rate limiting. Never log PHI in application or error logs.
Use HIPAA-eligible services on AWS, Azure, or Google Cloud with signed BAAs. Segment production from development — synthetic data in lower environments, never production PHI in staging. Backup and disaster recovery plans must include encrypted off-site copies and tested restore procedures.
Centralize logs in a SIEM. Alert on anomalous access patterns — bulk downloads, after-hours queries, failed authentication spikes. Document a 60-day breach notification workflow and run tabletop exercises annually.
Sateri Digital has delivered HIPAA-aware ERP, patient engagement, and clinical platforms for healthcare organizations worldwide. See our healthcare expertise or schedule a compliance architecture review with our team.
Common questions readers ask before planning implementation.
Start with a gap assessment against your current architecture, team capacity, and business goals. Prioritize one high-impact use case, validate outcomes, then scale in phases.
Most teams can identify early performance and workflow gains within the first 6 to 10 weeks when roadmap, ownership, and metrics are defined up front.
Track baseline metrics tied to business value: delivery speed, quality, operating cost, and user satisfaction. Use those metrics to guide scope and optimization decisions.
Yes. Security, compliance, and audit controls can be embedded into architecture and delivery practices from day one to support healthcare, finance, and other regulated domains.
Find the best way to choose suitable CRM software to manage your business.
October 2026
Legacy infrastructure costs, scaling bottlenecks, and compliance gaps — when to make the move.
March 2026
How to move from demos to production-grade ML systems that deliver measurable ROI.
February 2026